Cisco ASA AnyConnect vpn configuration with local authentication and vpn filter
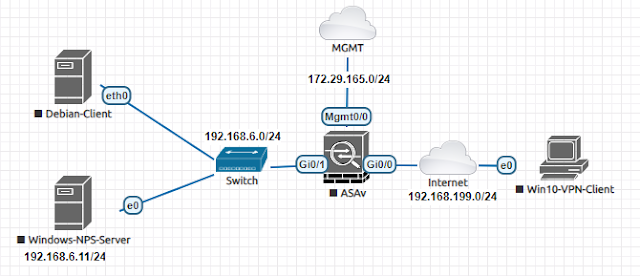
In this blog post, we will configure Cisco ASA firewall AnyConnect VPN. Remote users will be authenticated against ASA's local user database to get access to the VPN and traffic filtering/firewalling will be done using a vpn filter in ASA. Let's as usual introduce our topology - 01 - AnyConnect VPN Topology The topology is straight forward. We have a inside network (192.168.6.0/24). Outside network is 192.168.199.0/24 where the ASA listens for anyconnect connections. And a management network 172.29.165.0/24 which is just a out-of-band management network for ASA. We have a Win10-VPN-Client which will try to connect to inside network through anyconnect vpn. Debian-Client is just a client device in inside network to verify vpn connectivity. And Windows-NPS-Server is a radius server running NPS service. In this blog this nps server is not used. It will be used in the next blog when we move from local to radius authentication and vpn filter to dynamic acl. Basic network connecti...